The Bank of Ghana (BoG) has announced plans to conduct thematic reviews of banks’ compliance with its revised Cyber and Information Security Directive as concerns grow over digital financial fraud, cyber threats and other risks associated with electronic banking services.
The planned reviews are intended to strengthen cybersecurity oversight and improve the resilience of Ghana’s banking sector as more customers rely on digital platforms to access financial services.
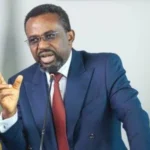
Governor of the Bank of Ghana, Dr Johnson Pandit Asiama, announced the initiative at the 43rd Annual General Meeting of the Ghana Association of Banks in Accra.
According to the Governor, cybersecurity, data protection, cloud computing, third-party dependencies and operational resilience are receiving increasing attention from the central bank as it responds to emerging risks in the financial sector.
“Digitalisation is transforming financial services. It has improved efficiency, convenience and financial inclusion, but it has also created new channels through which risks can emerge,” he said.
The planned reviews will assess banks’ compliance with the revised Cyber and Information Security Directive, which establishes cybersecurity requirements for financial institutions.
Dr Asiama said the central bank had continued to work with the Ghana Association of Banks and other industry players to facilitate the implementation of the revised directive.
The Governor also urged bank boards and senior management to treat cybersecurity and operational resilience as core business risks rather than issues that should be left solely to information technology departments. The directive comes at a time when financial institutions face increasingly interconnected risks involving digital infrastructure, external technology providers, data protection and the security of electronic transactions.
The central bank considers stronger risk-management frameworks essential to ensuring that banks can withstand emerging threats and maintain the reliability of their services and also emphasis on board-level accountability signals that cybersecurity must form part of broader institutional governance and risk management.
The reviews could help identify areas where institutions need to strengthen their controls and improve their preparedness for cyber incidents.
About The Author