
Microsoft and Japan’s National Police Agency (NPA) have disrupted a large cybercrime operation linked to more than one billion malicious messages targeting over 75,000 organisations across 150 countries.
According to investigators, more than 750 million malicious messages had been directed at Microsoft customers through email and SMS since the beginning of 2026.
The investigation uncovered what researchers described as a sprawling Chinese-language cybercrime marketplace offering tools and services used to launch phishing campaigns against individuals and organisations.
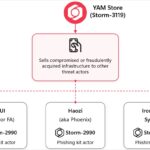
Investigators traced the activity to YAM Store, also known as Storm-3119, an underground marketplace providing infrastructure for cybercriminal operations. The investigation also linked the activity to phishing kits known as CoGUI, Haozi and Iron Man System, collectively tracked as Storm-2990.
These tools enable cybercriminals to conduct phishing campaigns designed to trick victims into revealing passwords, account credentials and other sensitive information.
Stolen credentials can subsequently be exploited to access email accounts, compromise corporate networks, steal financial information or facilitate further fraud.
The operation underscores the importance of international cooperation in disrupting cybercriminal infrastructure and protecting digital users from increasingly organised online threats.
About The Author